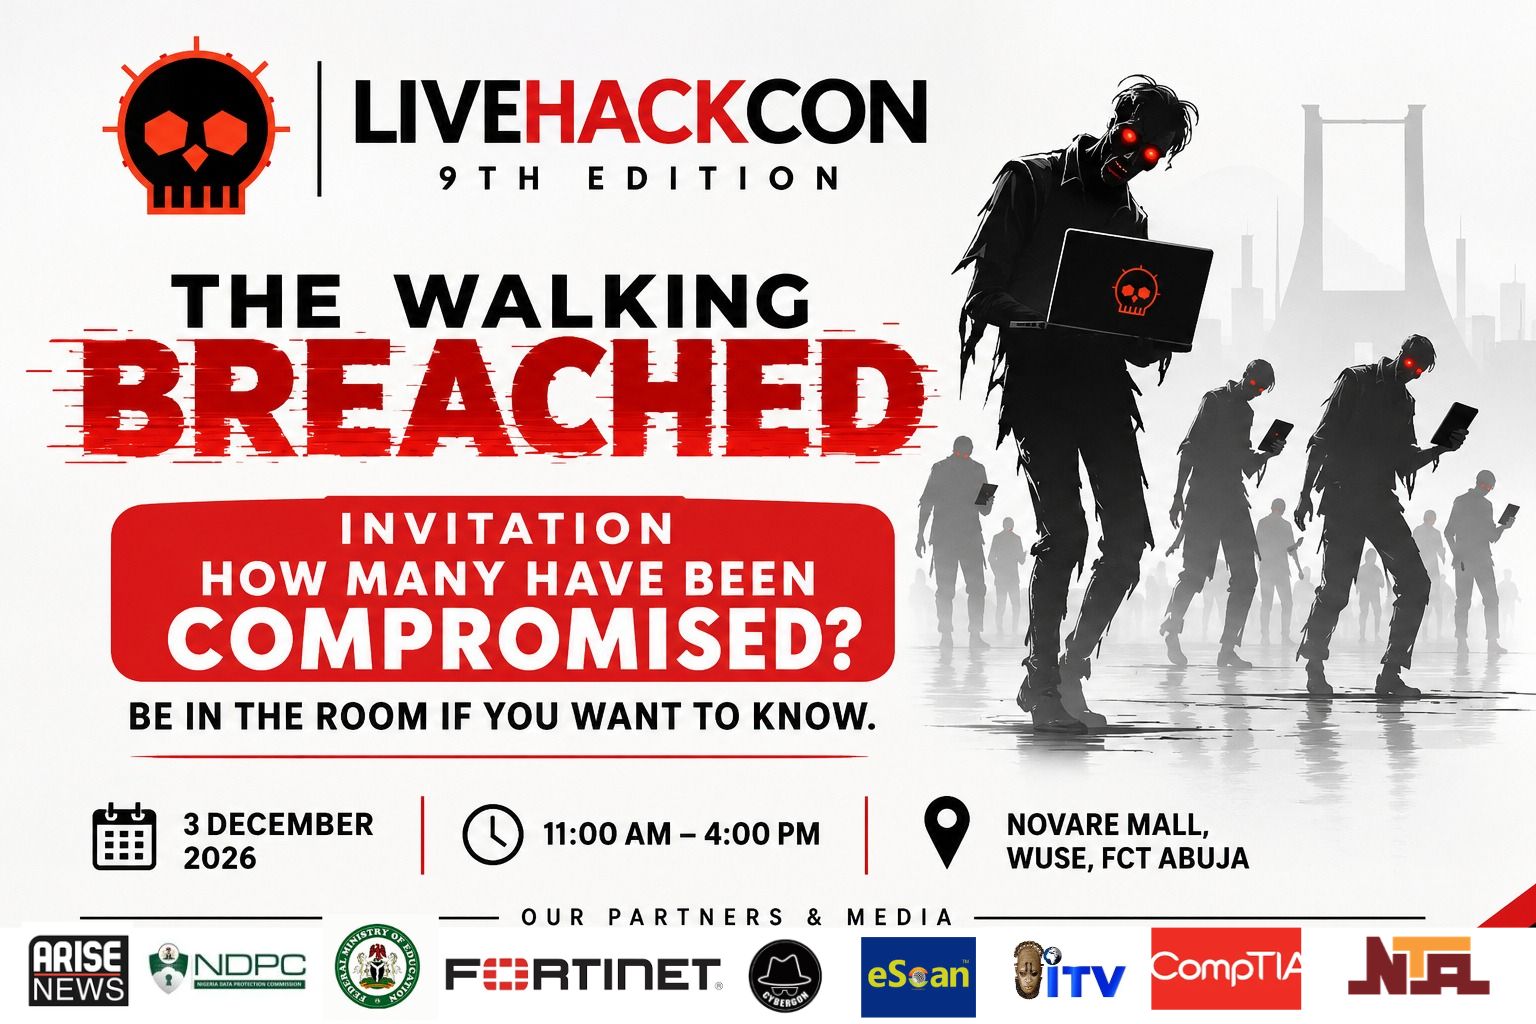
Abuja, Nigeria   /   03 December 2026THE WALKING BREACHED / HOW MANY ARE ALREADY COMPROMISED?
CYBERGON presents / 2026 edition

THE WALKING BREACHED.

The breach may already be inside. Quietly moving through forgotten accounts, infected endpoints, exposed servers, stolen credentials and systems nobody is watching. Like the walking dead, compromised systems can keep operating while the threat spreads. The question is no longer whether attacks happen. It is: how many are already infected, exposed or compromised, and who will detect them before it is too late?

03 DEC / 202611:00 AM – 4:00 PMABUJA / NIGERIA
COUNTDOWN TO THE LIVE EVENT
--Days
--Hours
--Minutes
--Seconds
LHCC_2026
THREAT_LEVEL: ACTIVE
LOCATION: NIGERIA
The infected are among us.
THE WALKING BREACHEDHOW MANY ARE COMPROMISED?FIND THE INFECTIONEXPOSE THE WEAKNESSDETECT. CONTAIN. DEFEND.THE WALKING BREACHEDHOW MANY ARE COMPROMISED?FIND THE INFECTIONEXPOSE THE WEAKNESSDETECT. CONTAIN. DEFEND.
WALKING BREACH / HOW COMPROMISE SPREADS — RESEARCH TOPICS
01 / RANSOMWARE Double-extortion operations
02 / CREDENTIALS Infostealers & session theft
03 / CLOUD Exposed storage & identity abuse
04 / PHISHING Business email compromise
05 / SUPPLY CHAIN Trusted-provider compromise
06 / BOTNETS DDoS-for-hire ecosystems
01 / RANSOMWARE Double-extortion operations
02 / CREDENTIALS Infostealers & session theft
03 / CLOUD Exposed storage & identity abuse
04 / PHISHING Business email compromise
05 / SUPPLY CHAIN Trusted-provider compromise
06 / BOTNETS DDoS-for-hire ecosystems
WHO MAY BE INSIDE? / ADVERSARY EXAMPLES FOR AWARENESS
APT28 State-linked espionage reporting
APT29 Espionage activity reporting
LAZARUS GROUP Financially motivated & espionage operations
SCATTERED SPIDER Social engineering & identity attacks

Curated threat themes and illustrative actor watchlist, not a live threat feed, current incident alert or attribution bulletin. Names are examples for education; verify current activity and attribution with trusted advisories before relying on them.

Nigeria threat intelligence

Where is the
breach hiding?

The map is an awareness guide to the kinds of digital environments where compromise can have serious consequences. Select a location to explore common exposure themes. It is not a live infection map or a count of compromised organisations.

NATIONAL CYBER THREAT MAP / NIGERIA

Potential infection pathways

Explore common exposure patterns across financial, government, education, energy and public-service environments. These are discussion prompts, not verified local incident reports.

Nigeria cyber threat awareness mapStylised outline of Nigeria with selectable markers for Lagos, Abuja, Kano, Port Harcourt, Enugu and Maiduguri. LAGOS ABUJA KANO PORT HARCOURT ENUGU MAIDUGURI
NIGERIA / REGIONAL THREAT AWARENESS VIEW
Threat themes for awarenessSelectable regional hubs
Select a location

Choose a marker on the map to explore common cyber risks relevant to that digital ecosystem.

Important: this is an illustrative awareness map, not a live attack feed, verified incident heat map or state-by-state risk ranking. The highlighted areas are not based on measured incident counts. No telemetry or visitor location is collected.

THREAT INTELLIGENCE / WATCH AREAS

What defenders should monitor

Threat themes that can affect organisations across Nigeria, regardless of location.

Identity attacksCredential theft · MFA fatigue
Financial threatsPayment fraud · BEC
RansomwareData theft · service disruption
Public exposureCloud assets · misconfigurations
Human targetingPhishing · social engineering
Critical servicesThird-party · supply-chain risk

Use current advisories from trusted national and sector response teams to validate threats before taking operational action.

01 / The conference

The breach is
already walking.

A compromised system does not always look compromised. It may still serve customers, process transactions and connect to trusted networks while an attacker quietly maintains access. The Walking Breached asks organisations to look beyond the perimeter and investigate what may already be inside.

Thursday
03 December 2026
11:00 AM
– 4:00 PM
Novare Mall
Wuse, Abuja
CYBERGON
LIMITED
SYSTEMS ALREADY INFECTED?UNKNOWN
ACCOUNTS COMPROMISED?UNKNOWN
EXPOSURE DETECTED?GO FIND OUT

No verified national infection or compromise total is being claimed on this page. The conference will use controlled demonstrations and evidence-led discussion to show how defenders can discover exposure.

The 2026 theme
THE
WALK
ING.

THE BREACH THAT NEVER LEFT.
THE ACCOUNT STILL ACTIVE.
THE SERVER STILL EXPOSED.

The idea behind the theme

A breach can be walking around inside your organisation long after the first compromise. It can hide in an endpoint, a cloud account, a forgotten server, a vendor connection or a privileged identity.

Inspired by the tension of a world where the infected are difficult to recognise, The Walking Breached turns the spotlight on silent compromise: systems that appear normal while attackers persist, move laterally, steal data or prepare their next move.

We will confront the uncomfortable question: how many devices, accounts, servers, applications and organisations are already compromised without knowing it? We will not invent a national infection figure. Instead, the conference will use controlled demonstrations, evidence-led discussion and practical investigation to show how exposure is discovered and what defenders can do next.

02 / Inside the experience

Find the infected.
Expose the breach.

Expect a high-energy, hands-on cybersecurity experience. Watch authorised live demonstrations, see how compromise occurs, learn how defenders detect suspicious activity and understand the decisions that limit damage.

[ 01 ]

Live hacking demonstrations

Watch controlled, authorised demonstrations that reveal how exposed services, weak configurations and vulnerable applications can be discovered and exploited, followed by defensive lessons.

[ 02 ]

How the infection spreads

Understand the paths attackers use: stolen credentials, phishing, unpatched systems, exposed remote access, malicious files and trusted third-party connections.

[ 03 ]

Compromise discovery

Explore practical indicators of compromise, suspicious authentication, persistence, lateral movement, unusual traffic and data exfiltration signals.

[ 04 ]

Containment & recovery

See how teams prioritise affected assets, isolate compromised systems, preserve evidence, eradicate threats and restore operations safely.

[ 05 ]

Real-world exposure

Examine risks around exposed servers, cloud storage, endpoints, identity systems, web applications, APIs and critical digital services.

[ 06 ]

Defence, compliance & accountability

Connect technical security with incident reporting, data protection duties, leadership accountability, resilience planning and organisational trust.

Looking back / 2025 edition

The last
data breach.

In 2025, the conference challenged organisations to think beyond the incident headline: understand what was exposed, how attackers got in, what defenders missed and what accountability looks like after a breach.

Watch highlights from the 2025 conference.

2025 / THE LAST DATA BREACH

What happens after the breach?

The 2025 edition, themed “The Last Data Breach… Hack, Defend and Comply”, brought the conversation to the point where technical compromise meets institutional responsibility. It examined the reality of exposed systems, the consequences of weak security practices, the importance of detection and response, and the role of data protection in rebuilding trust.

With participation and media attention from Nigeria’s broadcast landscape, including NTA, AIT, Arise News and Armed Forces Media, the conference continued CYBERGON’s commitment to taking cybersecurity out of theory and into public conversation.

The 2026 theme takes the next step: not only asking what was breached, but asking what may still be compromised right now.

Watch 2025 video ↗
03 / Who should attend

If you protect
digital systems,
you need to be
in this room.

For the people expected to find the breach, stop the spread, protect the organisation and explain what happened.

Government agencies & MDAs
CISOs & IT leaders
Cybersecurity teams
CSIRTs & SOC teams
Data protection officers
Risk & compliance leaders
Financial institutions
Telecoms & critical sectors
Academia & researchers
Technology professionals
In partnership with

INTERNATIONAL CYBERSECURITY
& AI RESEARCH CENTRE (ICARC)

Working together to advance cybersecurity, artificial intelligence research and threat intelligence through collaboration and knowledge exchange.

Department of Threat Intelligence

Discuss partnership ↗
Conference ecosystem

Built through
collaboration.

We welcome sponsors, institutional partners, research organisations, media collaborators and technology partners. Confirmed logos can be added here as participation is approved.

CYBERGONCONFERENCE ORGANISER
ICARCRESEARCH PARTNER
SPONSOR LOGORESERVED SLOT
PARTNER LOGORESERVED SLOT
COLLABORATORRESERVED SLOT

Sponsors and partners

04 / Be in the room

Will you find it
before it spreads?

Be part of The Walking Breached: an intense, practical conference experience built around live hacking demonstrations, compromise discovery, attack-path awareness, incident response, containment, threat intelligence, data protection and organisational accountability. Come ready to question assumptions, learn from practitioners, meet defenders and decision-makers, and leave with actions to strengthen your environment.

Live Hacking Cybersecurity Conference 2026

03 December 2026  ·  11:00 AM – 4:00 PM  ·  Novare Mall, Wuse, Abuja

Register now ↗

For registration, sponsorship, partnership or other arrangements: 08128141511  |  [email protected]

Privacy & data protection

Privacy policy

Effective date: 5 November 2026. This notice explains how CYBERGON LIMITED, as organiser of the Live Hacking Cybersecurity Conference 2026, may process personal information when you visit this website, contact the organisers or register for or attend the event. It is intended to align with the Nigeria Data Protection Act 2023 (NDPA) and, where applicable, the EU General Data Protection Regulation (GDPR).

1. Who is responsible?

Data controller: CYBERGON LIMITED. Event: Live Hacking Cybersecurity Conference 2026. Data Protection Officer contact: [email protected]. For event enquiries: [email protected].

2. Information we may process

Depending on how you interact with the organisers, information may include your name, work or organisation details, email address, telephone number, registration and attendance details, accessibility or dietary requests you choose to provide, correspondence, photographs or recordings made at the event, and basic technical information generated when you use this website. Please do not submit sensitive personal information unless it is necessary and specifically requested through an appropriate channel.

3. Why and on what basis?

Information may be used to respond to enquiries, administer registrations, communicate event changes, manage attendance and safety, provide requested event services, document and report on the conference, handle sponsorship or partnership enquiries, maintain website security and meet legal obligations. Depending on the specific activity, the lawful basis may be steps taken at your request or performance of a contract, legitimate interests balanced against your rights, compliance with a legal obligation, or your consent. Optional marketing and non-essential cookies are used only where you have given the required consent. You may withdraw consent at any time; this does not affect processing already carried out lawfully.

4. Cookies and similar technologies

Strictly necessary technologies support core website functions, security and your cookie choices. Optional analytics or advertising technologies should only be activated after you choose them in the cookie settings. You can accept all, reject optional cookies, or choose categories separately. Change your choice at any time using “Cookie settings” in the footer. This website's preference centre stores your choices locally; no analytics or advertising provider is configured in this preview. Before production launch, the organiser must list each actual cookie or tracker, its provider, purpose, duration and any associated data transfer.

5. Who may receive information?

Information may be made available only where necessary to authorised event staff and service providers supporting registration, hosting, communications, venue operations, security, photography or event delivery, and to competent authorities where required by law. Service providers should be bound by appropriate confidentiality and data-processing terms. We do not state that any particular third-party provider is engaged unless disclosed in the relevant registration or service notice.

6. International transfers

If information is accessed or stored outside Nigeria or the European Economic Area, the organiser will apply the transfer safeguards required by applicable law, such as an adequacy decision or appropriate contractual safeguards, and provide further information on request.

7. Retention and security

Personal information should be retained only for as long as necessary for the purposes described, including legitimate event administration, legal, accounting, security and dispute-resolution needs, and then securely deleted or anonymised. Appropriate technical and organisational safeguards are used to protect information. No website or transmission method can be guaranteed completely secure.

8. Your rights

Subject to applicable law and any relevant limitations, you may request access to your personal data, correction of inaccurate information, erasure, restriction of processing, portability, object to certain processing, and withdraw consent where consent is the basis. You may also complain to the Nigeria Data Protection Commission and, where the GDPR applies, your competent EU/EEA supervisory authority. Contact the DPO at [email protected] to exercise a right or ask a question. We may need to verify your identity before responding.

9. Children

This conference website and event communications are not designed to solicit personal information from children. If information about a child is required for a specific event purpose, the organiser will apply the additional safeguards and consent requirements imposed by applicable law.

10. Updates and contact

This notice may be updated when event operations or legal requirements change. The current version will be published on this page. Privacy questions and data subject requests: [email protected].

Important: this is a website privacy notice template based on the information currently supplied. Before publishing, CYBERGON LIMITED should verify the actual registration form fields, processors, hosting location, cookie inventory, retention periods, marketing practices, photography notices and international transfers. This notice is not a certification of compliance or legal advice.
Privacy & cookie settings